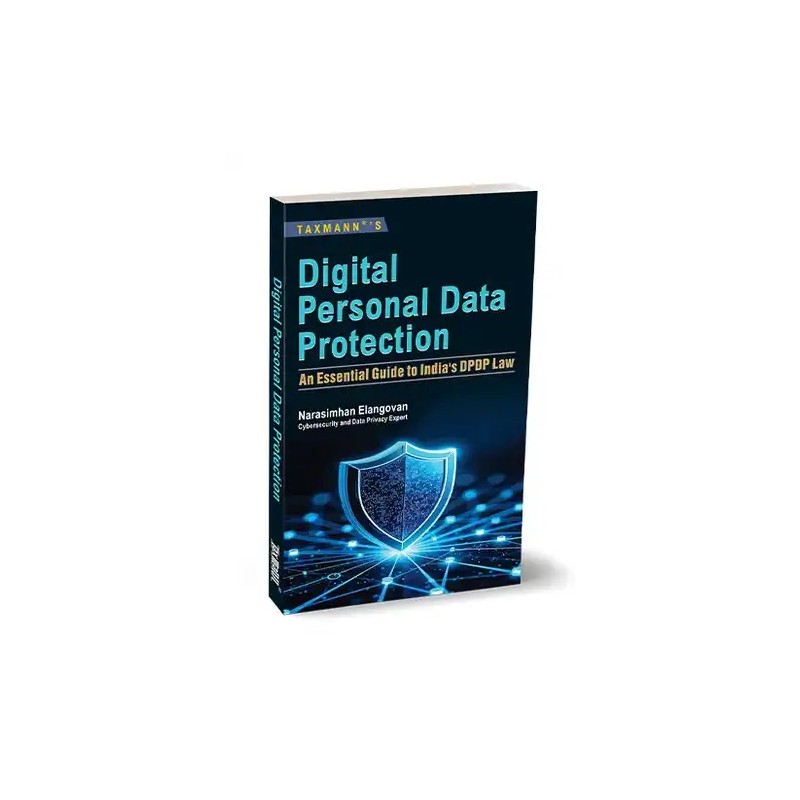
Digital Personal Data Protection By Narasimhan Elangovan
Digital Personal Data Protection – An Essential Guide to India's DPDP Law is a practitioner's guide to the Digital Personal Data Protection Act 2023 and the Digital Personal Data Protection Rules 2025. It is written for professionals who must make compliance happen, and it takes them from the statutory text to a working programme: what must change, who must be accountable, and what evidence proves compliance.
The book is written for the period before enforcement begins, when organisations must design compliance without Indian precedent to guide them. It bridges the text of the law and the reality of its implementation, and answers practical questions that cut across legal, technology, and business functions.
The result is a working reference for building data-governance programmes that earn and preserve trust in India's fast-evolving digital economy.
This book is intended for the following audience:
- Chartered Accountants advising clients on DPDP compliance
- Company Secretaries briefing boards on data protection obligations
- Internal Auditors and Independent Data Auditors assessing DPDP readiness
- Data Protection Officers, Privacy Officers, and Compliance and Risk Professionals building governance frameworks
- Chief Information Security Officers strengthening technical safeguards and breach response
- In-house Lawyers interpreting the Act and the Rules for their organisations
- HR Leaders responsible for employee data
- Technology and Product Leaders embedding privacy into systems and processes
The Present Publication is the 2026 Edition, authored by CA Narasimhan Elangovan. The law stated in this book is as updated till 15th September 2026, with the following noteworthy features:
- [Anchored in the Text] The analysis is anchored in the text of the Act and the Rules, cited down to the section, sub-section, clause and rule, rather than in summaries or secondary commentary
- [Recurring Disciplines] Across its implementation sections, the book returns to the same habits: classify each processing activity separately, record who decided and when, and review at least annually and whenever a material change occurs
- [Illustrative Templates] Thirteen templates give working formats, from a model notice and a Data Processing Agreement clause checklist to a Data Protection Impact Assessment (DPIA) structure, a first-90-days readiness checklist and a Board inquiry response protocol. They are designed as starting points, to be adapted to each organisation, reviewed by legal counsel and maintained as living documents
- [Audit Considerations] Twelve chapters (3 to 14) state what an auditor will test and list the findings that recur in practice, 57 in all. Eight of them (Chapters 3 to 10) also list the evidence to keep ready. The guidance serves both the organisation preparing for an audit and the auditor conducting one
- [Consolidated Requirements Register] Appendix A restates the obligations under the Act and the Rules as 49 testable requirements across 15 subject areas. Each carries its legal reference and a numbered list of audit evidence, 239 items in all, ranging from registers, logs and screenshots to sign-offs and test results. Obligations that apply only to Significant Data Fiduciaries are marked, and Consent Manager obligations are grouped separately. It is built to work as a structured checklist, so that no obligation is overlooked
- [Case Study Boxes] Thirty boxed notes (case studies, comparative notes, practical scenarios and short explainers) support the analysis. The case studies draw on decisions of the Supreme Court of India and the Court of Justice of the European Union, and on enforcement actions by regulators in France, Norway, Portugal and Ireland. The comparative notes set the book's analysis against the GDPR, the EU AI Act and the RBI Account Aggregator framework, and flag where habits formed under the GDPR do not carry over
- [Regulatory Overlap Mapping] The book shows how to map DPDP duties against existing obligations, such as those set by the RBI, SEBI, IRDAI and CERT-In, one obligation at a time: where they overlap, where the Act adds to them, where they conflict, which requirement is more restrictive, and which control satisfies both. It also shows how far existing ISO 27001 and SOC 2 controls go, and where gaps remain
- [Worked Scenarios] Scenarios from everyday Indian practice make the discussion concrete. They include a compliance officer at a mid-size NBFC asking on what basis data is being processed, a chartered accountant handling a client's tax return, a paper visitor register that is later scanned, an e-commerce breach confirmed at 9 a.m. on a Monday, and a steering committee formed only in January 2027
The coverage of the book is as follows:
- Part I | The Law and its Architecture
- Genesis and Framework of the DPDP Act 2023 (Chapter 1) — Orients the reader to the Act's origins, design and regulatory architecture. It reduces territorial scope to a two-question applicability test, maps the Rules against the Act they operationalise, and turns the phased commencement into a backward plan with named long-lead workstreams.
- Key Definitions and Foundational Concepts (Chapter 2) — Treats the defined terms that carry the most compliance weight as operational triggers, not academic labels. It gives tests for telling a Data Fiduciary from a Data Processor, a register and a five-field record for role decisions, a five-step board method for choices the statute leaves open, and the case for assessing Significant Data Fiduciary status early
- Part II | Obligations of Data Fiduciaries
- Grounds for Legal Processing (Chapter 3) — Shows how to classify every processing activity before processing begins. It supplies a five-question test of consent validity, a clause-by-clause guide to the legitimate uses with examples of what falls in and out, and a routine for building and reviewing the lawful basis register
- Notice and Consent (Chapter 4) — Treats notice and consent as drafting and system-design work. It contrasts vague and specific notice wording, lays out a staged translation plan, measures withdrawal against consent in steps, screens, clicks and time, specifies consent record fields with periodic integrity checks, and plans the transitional notice rollout as a project with milestones
- General Obligations of a Data Fiduciary (Chapter 5) — Explains what a governance charter and a Data Processor register should cover, and sets out validation rules for data quality and a grievance workflow with graduated internal timelines and audit-ready records
- Security Safeguards and Breach Management (Chapter 6) — Takes the minimum safeguards one clause at a time, then gives a system-by-system gap assessment that rates each control as existing, partial or absent. It also covers a breach response workflow with defined decision, notification and investigation roles, tabletop exercises at least once a year across four breach scenarios, pre-drafted breach intimations and a log retention design
- Processing of Children's Data and Data of Persons with Disability (Chapter 7) — Covers age-gating that goes beyond self-declaration, a screening question for identity-verification vendors, a verification record for each child account, system-level controls that keep child accounts out of tracking and targeted advertising, a child well-being impact assessment, an exemption register and a guardian verification procedure
- Retention, Deletion, and Cross-Border Transfer (Chapter 8) — Shows how to build a retention schedule that reconciles DPDP retention with other laws, run a six-step pre-deletion notification workflow, contract for erasure by Data Processors, find incidental transfers (disaster-recovery copies, multi-region cloud hosting, remote support access and CDN caching), and record them in a transfer register
- Part III | Rights of Data Principals
- Rights, Duties, and the Grievance Framework (Chapter 9) — Sets out a six-stage rights workflow from intake to closure with suggested internal service levels, the contents of a reasoned refusal, a register of declined and deferred erasures, a nomination design with nominee verification, and identity checks kept proportionate to risk
- Part IV | Significant Data Fiduciaries and Special Provisions
- Significant Data Fiduciaries - Additional Obligations (Chapter 10) — Treats the DPO appointment as a senior governance decision with defined terms of reference. It applies an auditor-independence test drawn from audit practice, specifies the auditor's engagement letter, builds a DPIA methodology, sets an annual compliance calendar counted back from each deadline, and illustrates algorithmic risk through recommendation engines and credit-scoring models
- Exemptions and Special Provisions (Chapter 11) — Maps the exemptions layer by layer, with a running focus on what still applies. It supplies an exemption register with three worked entries, a research processing protocol and a routine for tracking new notifications
- Part V | Compliance and Enforcement
- The Compliance Programme – Planning, Governance, and Readiness (Chapter 12) — Turns the preceding chapters into a programme: a three-phase roadmap against May 2027, priorities for the first ninety days, three-tier governance, a minimum set of eight policies, two-tier training, an evidence framework built on six types of artefact, and readiness for a Board inquiry
- Sector-Specific Considerations (Chapter 13) — Examines eight sectors, from banking and insurance to SaaS and co-operative banks, with a separate note on SEBI-regulated entities. Its angles include lawful basis mapping across the insurance policy lifecycle, purpose-by-purpose consent design for large e-commerce platforms, tenant-level data residency for SaaS providers and a foundation-first path for smaller institutions. It draws out three implementation considerations that apply across all sectors
- Enforcement, Penalties, and Dispute Resolution (Chapter 14) — Walks through an enforcement action in the order it would unfold, uses the penalty factors to show where compliance investment matters most, and prepares the reader for the Board's digital office and for the voluntary undertaking as a strategic option
- Glossary and Appendices
- Glossary of Defined Terms — 22 terms, arranged alphabetically, each with its statutory reference
- Appendix A — Consolidated Requirements Register
- Appendix B — Full text of the Digital Personal Data Protection Act 2023, with 54 Section Notes on Sections 1 to 9. The notes answer common questions, set the Act against section 43A of the IT Act and the SPDI Rules, and flag the exemption and penalty position for Sections 4 to 8
- Appendix C — Full text of the Digital Personal Data Protection Rules 2025, with the seven Schedules
- Appendix D — The three notifications of 13th November 2025 on commencement, and on the establishment and composition of the Board